Want to know Certleader MS-102 Exam practice test features? Want to lear more about Microsoft Microsoft 365 Administrator Exam certification experience? Study Realistic Microsoft MS-102 answers to Regenerate MS-102 questions at Certleader. Gat a success with an absolute guarantee to pass Microsoft MS-102 (Microsoft 365 Administrator Exam) test on your first attempt.
Online MS-102 free questions and answers of New Version:
NEW QUESTION 1
You need to ensure that User1 can enroll the devices to meet the technical requirements. What should you do?
- A. From the Azure Active Directory admin center, assign User1 the Cloud device administrator rote.
- B. From the Azure Active Directory admin center, configure the Maximum number of devices per user setting.
- C. From the Intune admin center, add User1 as a device enrollment manager.
- D. From the Intune admin center, configure the Enrollment restrictions.
Answer: C
Explanation:
References:
https://docs.microsoft.com/en-us/sccm/mdm/deploy-use/enroll-devices-with-device-enrollment-manager
NEW QUESTION 2
DRAG DROP
Your company has a Microsoft 365 E5 tenant.
Users access resources in the tenant by using both personal and company-owned Android devices. Company policies requires that the devices have a threat level of medium or lower to access Microsoft Exchange Online mailboxes.
You need to recommend a solution to identify the threat level of the devices and to control access of the devices to the resources.
What should you include in the solution for each device type? To answer, drag the appropriate components to the correct devices. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.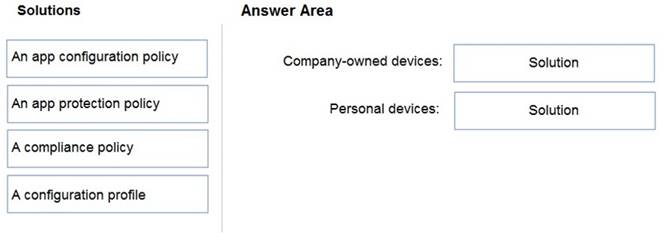
Solution:
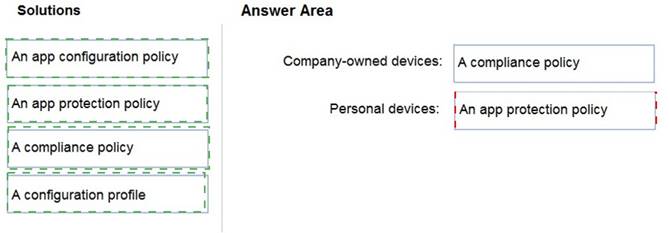
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 3
You have a Microsoft 365 E3 subscription that uses Microsoft Defender for Endpoint Plan 1.
Which two Defender for Endpoint features are available to the subscription? Each correct
answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. advanced hunting
- B. security reports
- C. digital certificate assessment
- D. device discovery
- E. attack surface reduction (ASR)
Answer: BE
Explanation:
B: Overview of Microsoft Defender for Endpoint Plan 1, Reporting
The Microsoft 365 Defender portal (https://security.microsoft.com) provides easy access to information about detected threats and actions to address those threats.
The Home page includes cards to show at a glance which users or devices are at risk, how many threats were detected, and what alerts/incidents were created.
The Incidents & alerts section lists any incidents that were created as a result of triggered alerts. Alerts and incidents are generated as threats are detected across devices.
The Action center lists remediation actions that were taken. For example, if a file is sent to quarantine, or a URL is blocked, each action is listed in the Action center on the History tab.
The Reports section includes reports that show threats detected and their status. E: What can you expect from Microsoft Defender for Endpoint P1?
Microsoft Defender for Endpoint P1 is focused on prevention/EPP including:
Next-generation antimalware that is cloud-based with built-in AI that helps to stop ransomware, known and unknown malware, and other threats in their tracks.
(E) Attack surface reduction capabilities that harden the device, prevent zero days, and offer granular control over access and behaviors on the endpoint.
Device based conditional access that offers an additional layer of data protection and breach prevention and enables a Zero Trust approach.
The below table offers a comparison of capabilities are offered in Plan 1 versus Plan 2.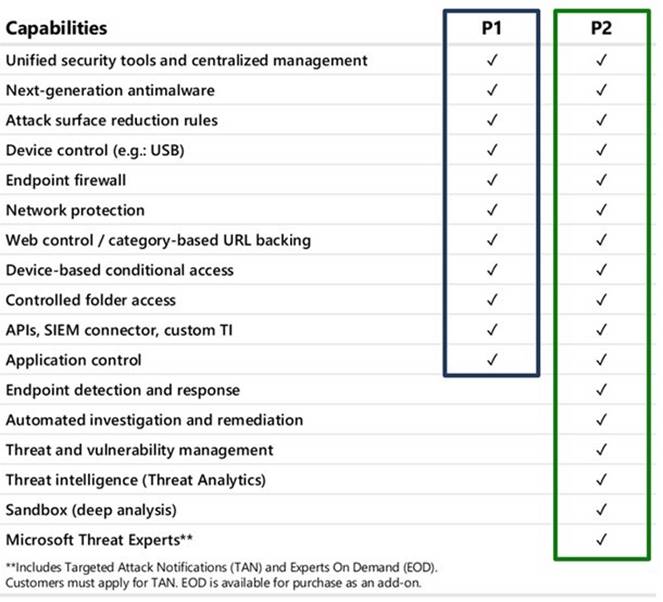
Incorrect:
Not A: P2 is by far the best fit for enterprises that need an EDR solution including automated investigation and remediation tools, advanced threat prevention and threat and vulnerability management (TVM), and hunting capabilities.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/defender-endpoint/defender- endpoint-plan-1
https://techcommunity.microsoft.com/t5/microsoft-defender-for-endpoint/microsoft-defender-for-endpoint-plan-1-now-included-in-m365-e3/ba-p/3060639
NEW QUESTION 4
HOTSPOT
You have a Microsoft 365 E5 subscription that contains 200 Android devices enrolled in Microsoft Intune.
You create an Android app protection policy named Policy! that is targeted to all Microsoft apps and assigned to all users.
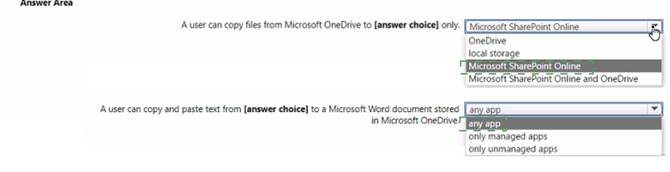
Policy! has the Data protection settings shown in the following exhibit.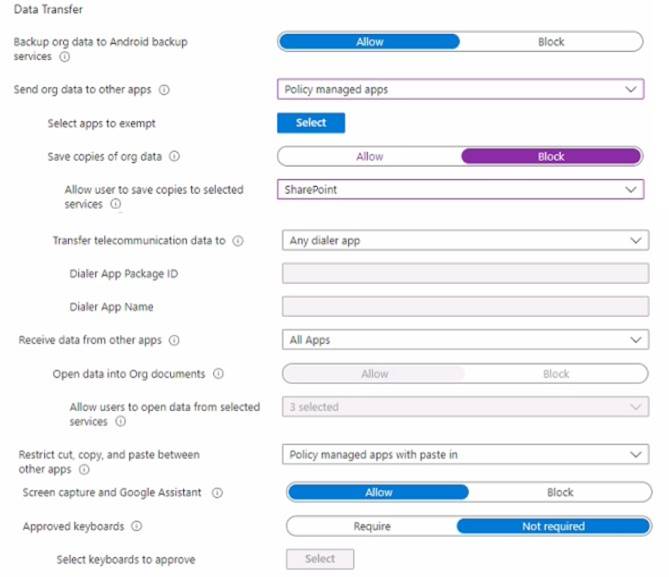
Use the drop-down menus to select 'he answer choice that completes each statement based on the information presented in the graphic.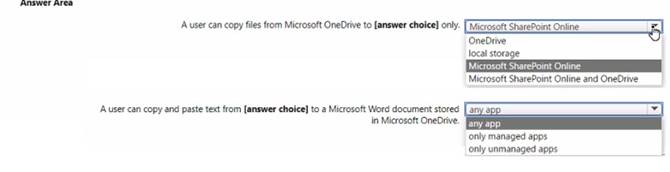
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 5
HOTSPOT
You have a Microsoft 365 E5 tenant that uses Microsoft Intune. You need to configure Intune to meet the following requirements:
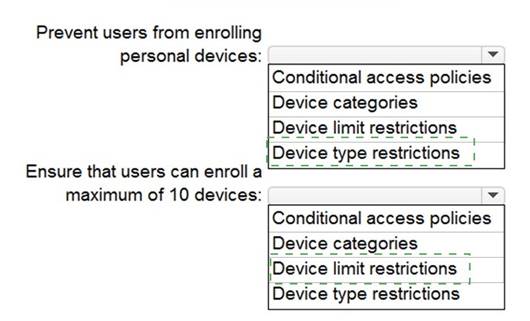
✑ Prevent users from enrolling personal devices.
✑ Ensure that users can enroll a maximum of 10 devices.
What should you use for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.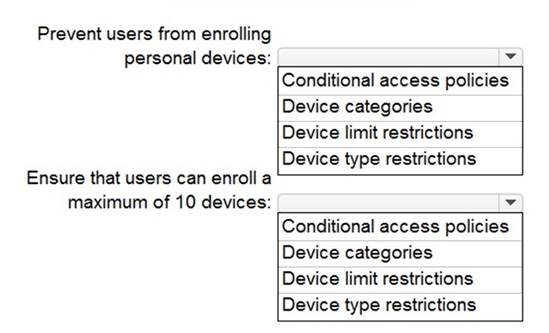
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 6
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
From the Microsoft 365 Defender, you create a role group named US eDiscovery Managers by copying the eDiscovery Manager role group.
You need to ensure that the users in the new role group can only perform content searches of mailbox content for users in the United States.
Solution: From the Microsoft 365 Defender, you modify the roles of the US eDiscovery Managers role group.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION 7
HOTSPOT
HOTSPOT
You have a Microsoft 365 subscription that contains the users shown in the following table.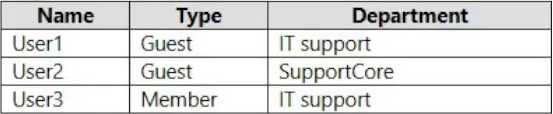
You need to configure a dynamic user group that will include the guest users in any department that contains the word Support.
How should you complete the membership rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.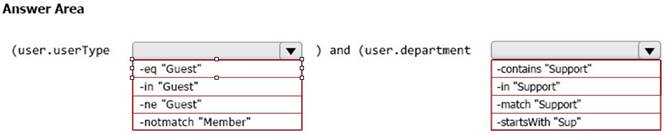
Solution:
Box 1: -eq "Guest"
Dynamic membership rules for groups in Azure Active Directory
Supported expression operators
The following table lists all the supported operators and their syntax for a single expression. Operators can be used with or without the hyphen (-) prefix. The Contains operator does partial string matches but not item in a collection matches.
* Equals
-eq
* Contains
-contains
* Etc.
Box 2: -contains "Support" Incorrect:
* -in
If you want to compare the value of a user attribute against multiple values, you can use
the -in or -notIn operators.
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 8
You need to create the Safe Attachments policy to meet the technical requirements. Which option should you select?
- A. Replace
- B. Enable redirect
- C. Block
- D. Dynamic Delivery
Answer: D
Explanation:
Reference:
https://github.com/MicrosoftDocs/microsoft-365-docs/blob/public/microsoft-365/security/office-365-security/safe-attachments.md
NEW QUESTION 9
Your network contains an Active Directory forest named contoso.local. You purchase a Microsoft 365 subscription.
You plan to move to Microsoft 365 and to implement a hybrid deployment solution for the next 12 months.
You need to prepare for the planned move to Microsoft 365.
What is the best action to perform before you implement directory synchronization? More than one answer choice may achieve the goal. Select the BEST answer.
- A. Purchase a third-party X.509 certificate.
- B. Create an external forest trust.
- C. Rename the Active Directory forest.
- D. Purchase a custom domain name.
Answer: D
Explanation:
The first thing you need to do before you implement directory synchronization is to purchase a custom domain name. This could be the domain name that you use in your on- premise Active Directory if it’s a routable domain name, for example, contoso.com.
If you use a non-routable domain name in your Active Directory, for example contoso.local, you’ll need to add the routable domain name as a UPN suffix in Active Directory.
Incorrect:
Not C: No need to rename the Active Directory forest. As we use a non-routable domain name contoso.local, we just need to add the routable domain name as a UPN suffix in Active Directory.
Reference:
https://docs.microsoft.com/en-us/office365/enterprise/set-up-directory-synchronization
NEW QUESTION 10
You plan to use Azure Sentinel and Microsoft Cloud App Security. You need to connect Cloud App Security to Azure Sentinel.
What should you do in the Cloud App Security admin center?
- A. From Automatic log upload, add a log collector.
- B. From Automatic log upload, add a data source.
- C. From Connected apps, add an app connector.
- D. From Security extension, add a SIEM agent.
Answer: D
NEW QUESTION 11
HOTSPOT
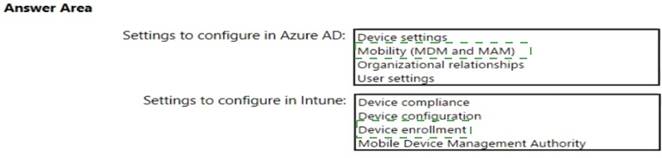
You need to meet the technical requirements and planned changes for Intune. What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.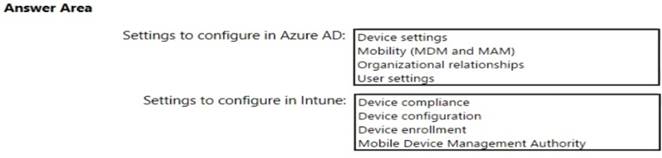
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 12
HOTSPOT
HOTSPOT
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1. Site1 has he files in the following table.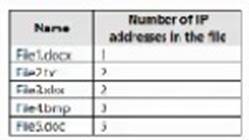
The Site1 users are assigned the roles shown in the following table.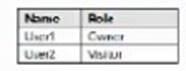
You create a data less prevention (DLP) policy names Policy1 as shown in the following exhibit.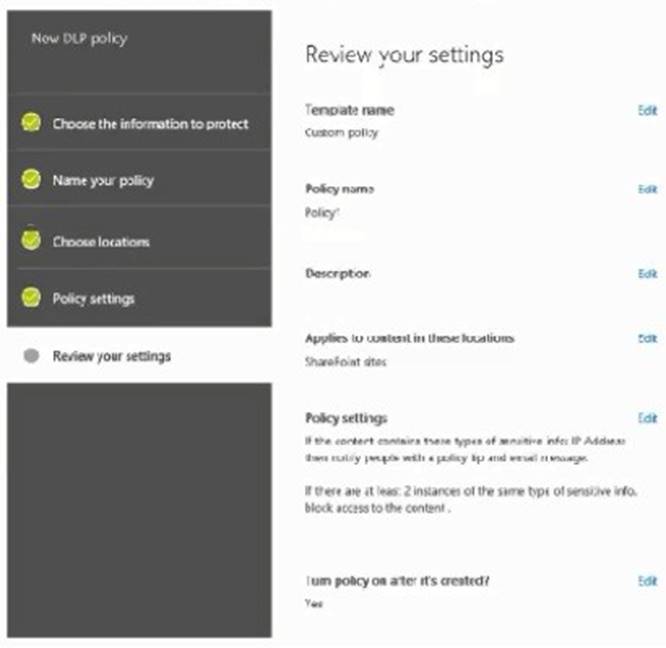
How many files will be visible to user1 and User2 after Policy' is applied to answer, selected select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.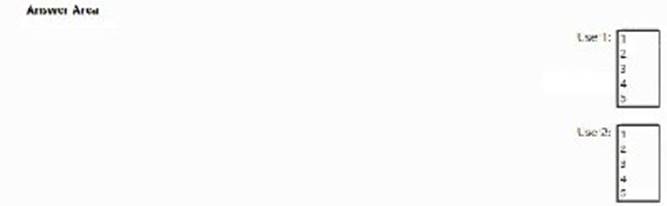
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 13
HOTSPOT
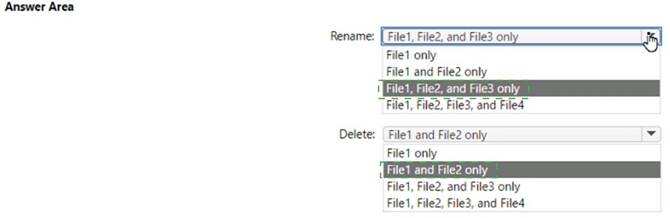
You have a Microsoft 365 subscription that contains a user named User1 and a Microsoft SharePoint Online site named Site1. User1 is assigned the Owner role for Site1. To Site1, you publish the file plan retention labels shown in the following table.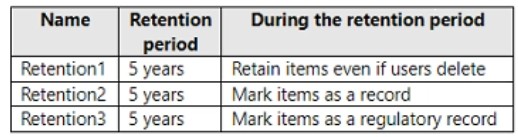
Site1 contains the files shown in the following table.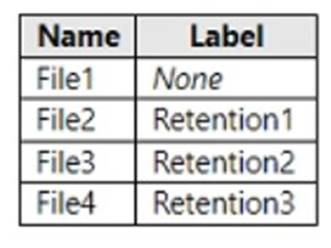
Which files can User1 rename, and which files can User1 delete? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.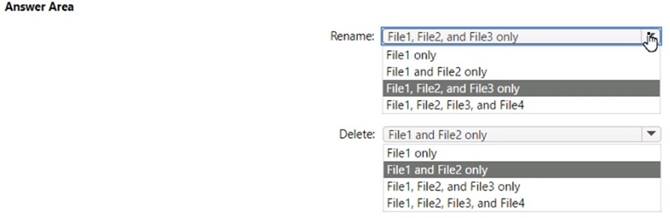
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 14
FILL IN THE BLANK
You have a Microsoft 365 subscription.
From Microsoft 365 Defender, you create a role group named US eDiscovery Managers by copying the eDiscovery Manager role group.
You need to ensure that the users in the new role group can only perform content searches of mailbox content for users in the United States.
Solution: From Windows PowerShell, you run the New-complianceSecurityFilter cmdlet with the appropriate parameters.
Does this meet the goal?
A Yes
- A. No
Answer: A
NEW QUESTION 15
HOTSPOT
You have a Microsoft 365 E5 tenant.
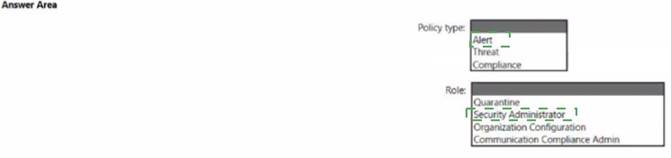
You need to ensure that administrators are notified when a user receives an email message that contains malware. The solution must use the principle of least privilege.
Which type of policy should you create and which Microsoft 365 compliance center role is required to create the pokey? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.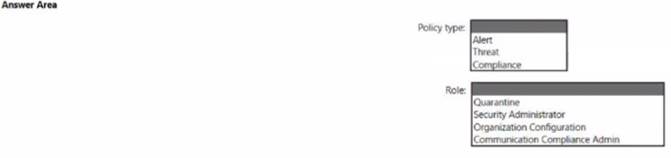
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 16
HOTSPOT
Your company has a Microsoft 365 E5 tenant.
Users at the company use the following versions of Microsoft Office:
• Microsoft 365 Apps for enterprise
• Office for the web
• Office 2016
• Office 2019
The company currently uses the following Office file types:
• .docx
• .xlsx
• .doc
• xls
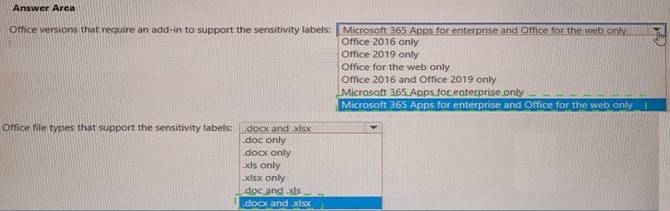
You plan to use sensitivity labels. You need to identify the following:
• Which versions of Office require an add-in to support the sensitivity labels.
• Which file types support the sensitivity labels.
What should you identify? To answer, select the appropriate options in the answer area, NOTE: Each correct selection is worth one point.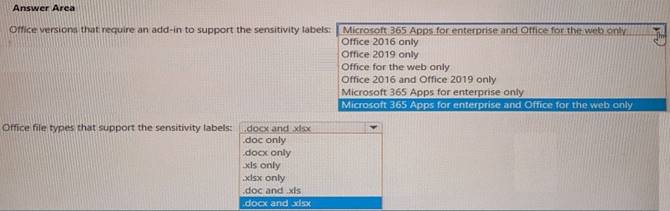
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 17
You have a Microsoft 365 subscription that uses an Azure AD tenant named contoso.com. The tenant contains the users shown in the following table.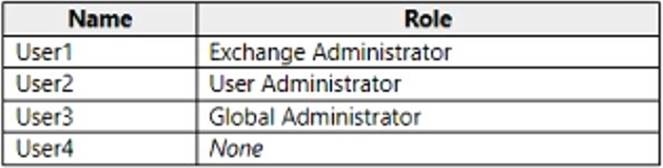
You add another user named User5 to the User Administrator role. You need to identify which two management tasks User5 can perform.
Which two tasks should you identify? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Delete User2 and User4 only.
- B. Reset the password of User4 only
- C. Reset the password of any user in Azure AD.
- D. Delete User1, User2, and User4 only.
- E. Reset the password of User2 and User4 only.
- F. Delete any user in Azure AD.
Answer: AE
Explanation:
Users with the User Administrator role can create users and manage all aspects of users with some restrictions (see below).
Only on users who are non-admins or in any of the following limited admin roles:
• Directory Readers
• Guest Inviter
• Helpdesk Administrator
• Message Center Reader
• Reports Reader
• User Administrator Reference:
https://docs.microsoft.com/en-us/azure/active-directory/users-groups-roles/directory-assign-admin-roles#available-roles
NEW QUESTION 18
You have a Microsoft 365 E5 subscription. You need to create a mail-enabled contact. Which portal should you use?
- A. the Microsoft 365 admin center
- B. the SharePoint admin center
- C. the Microsoft Entra admin center
- D. the Microsoft Purview compliance portal
Answer: A
NEW QUESTION 19
You have a Microsoft 365 E5 subscription.
You plan to create a data loss prevention (DLP) policy that will be applied to all available locations.
Which conditions can you use in the DLP rules of the policy?
- A. sensitive info types
- B. content search queries
- C. keywords
- D. sensitivity labels
Answer: C
Explanation:
Apply retention labels to content automatically if it matches specific conditions, that includes cloud attachments that are shared in email or Teams, or when the content contains:
Specific types of sensitive information.
Specific keywords that match a query you create.
Pattern matches for a trainable classifier.
Note: Retention policies can be applied to the following locations: Exchange mailboxes
SharePoint classic and communication sites OneDrive accounts
Microsoft 365 Group mailboxes & sites Skype for Business
Exchange public folders
Teams channel messages (standard channels and shared channels) Teams chats
Teams private channel messages Yammer community messages Yammer user messages
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/retention https://learn.microsoft.com/en-us/microsoft-365/compliance/dlp-exchange-conditions-and-
actions
NEW QUESTION 20
......
Recommend!! Get the Full MS-102 dumps in VCE and PDF From Dumpscollection.com, Welcome to Download: https://www.dumpscollection.net/dumps/MS-102/ (New 463 Q&As Version)