It is more faster and easier to pass the Paloalto-Networks PCNSE exam by using Practical Paloalto-Networks Palo Alto Networks Certified Security Engineer (PCNSE)PAN-OS 9.0 questuins and answers. Immediate access to the Avant-garde PCNSE Exam and find the same core area PCNSE questions with professionally verified answers, then PASS your exam with a high score now.
Free demo questions for Paloalto-Networks PCNSE Exam Dumps Below:
NEW QUESTION 1
Refer to the exhibit.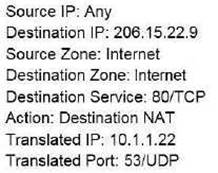
Using the above screenshot of the ACC, what is the best method to set a global filter, narrow down Blocked User Activity, and locate the user(s) that could be compromised by a botnet?
- A. Click the hyperlink for the Zero Access.Gen threat.
- B. Click the left arrow beside the Zero Access.Gen threat.
- C. Click the source user with the highest threat count.
- D. Click the hyperlink for the hotport threat Category.
Answer: B
Explanation:
Hover over an attribute in the table below the chart and click the arrow icon to the right of the attribute. https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/monitoring/use-the-application-command-center/int
NEW QUESTION 2
An engineer reviews high availability (HA) settings to understand a recent HA failover event. Review the screenshot below.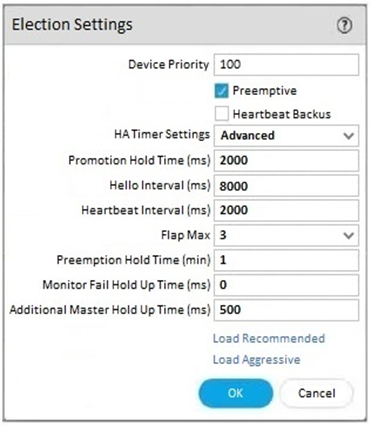
Which timer determines the frequency at which the HA peers exchange messages in the form of an ICMP (ping)
- A. Hello Interval
- B. Promotion Hold Time
- C. Heartbeat Interval
- D. Monitor Fail Hold Up Time
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/high-availability/ha-concepts/ha-timers
NEW QUESTION 3
What is the best definition of the Heartbeat Interval?
- A. The interval in milliseconds between hello packets
- B. The frequency at which the HA peers check link or path availability
- C. The frequency at which the HA peers exchange ping
- D. The interval during which the firewall will remain active following a link monitor failure
Answer: C
Explanation:
The firewalls exchange hello messages and heartbeats at configurable intervals to verify that the peer firewall is responsive and operational. Hello messages are sent from one peer to the other to verify the state of the firewall. The heartbeat is an ICMP ping to the HA peer. A response from the peer indicates that the firewalls are connected and responsive.
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClUcCAK
"A "heartbeat-interval" CLI command was added to the election settings for HA, this interval has a 1000ms minimum for all Palo Alto Networks platforms and is an ICMP ping to the other device through the HA control link." https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClMaCAK
NEW QUESTION 4
Which User-ID mapping method should be used in a high-security environment where all IP address-to-user mappings should always be explicitly known?
- A. PAN-OS integrated User-ID agent
- B. GlobalProtect
- C. Windows-based User-ID agent
- D. LDAP Server Profile configuration
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/user-id/user-id-concepts/user-mapping/globalprote GlobalProtect is a VPN solution that provides secure remote access to corporate networks. When a user connects to GlobalProtect, their identity is verified against an LDAP server. This ensures that all IP address-to-user mappings are explicitly known.
NEW QUESTION 5
An administrator has configured a pair of firewalls using high availability in Active/Passive mode. Link and Path Monitoring is enabled with the Failure Condition set to "any." There is one link group configured containing member interfaces ethernet1/1 and ethernet1/2 with a Group Failure Condition set to "all."
Which HA state will the Active firewall go into if ethernet1/1 link goes down due to a failure?'
- A. Active-Secondary
- B. Non-functional
- C. Passive
- D. Active
Answer: D
NEW QUESTION 6
A network security administrator has been tasked with deploying User-ID in their organization. What are three valid methods of collecting User-ID information in a network? (Choose three.)
- A. Windows User-ID agent
- B. GlobalProtect
- C. XMLAPI
- D. External dynamic list
- E. Dynamic user groups
Answer: ABC
Explanation:
User-ID is a feature that allows the firewall to identify and classify users and groups on the network based on their usernames, IP addresses, and other attributes1. User-ID information can be collected from various sources, such as: A: Windows User-ID agent: A software agent that runs on a Windows server and collects user information from Active Directory domain controllers, Exchange servers, or eDirectory servers2. The agent then sends the user information to the firewall or Panorama for user mapping2. B: GlobalProtect: A software agent that runs on the endpoints and provides secure VPN access to the network3. GlobalProtect also collects user information from the endpoints and sends it to the firewall or Panorama for user mapping4. C: XMLAPI: An application programming interface that allows external systems or scripts to send user information to the firewall or Panorama in XML format. The XMLAPI can be used to integrate with third-party systems, such as identity providers, captive portals, or custom applications.
NEW QUESTION 7
During the process of developing a decryption strategy and evaluating which websites are required for corporate users to access, several sites have been identified that cannot be decrypted due to technical reasons. In this case, the technical reason is unsupported ciphers Traffic to these sites will therefore be blocked if decrypted.
How should the engineer proceed?
- A. Install the unsupported cipher into the firewall to allow the sites to be decrypted
- B. Allow the firewall to block the sites to improve the security posture.
- C. Add the sites to the SSL Decryption Exclusion list to exempt them from decryption.
- D. Create a Security policy to allow access to those sites.
Answer: C
Explanation:
If some sites cannot be decrypted due to technical reasons, such as unsupported ciphers, and blocking them is not an option, then the engineer should add the sites to the SSL Decryption Exclusion list to exempt them from decryption. The SSL Decryption Exclusion list is a predefined list of sites that are not subject to SSL decryption by the firewall. The list includes sites that use certificate pinning, mutual authentication, or unsupported cipher suites. The engineer can also add custom sites to the list if they have a valid business reason or technical limitation for not decrypting them34. Adding the sites to the SSL Decryption Exclusion list will allow the traffic to pass through without being decrypted or blocked by the firewall. References: SSL Decryption Exclusion, Troubleshoot Unsupported Cipher Suites
NEW QUESTION 8
Which operation will impact the performance of the management plane?
- A. Decrypting SSL sessions
- B. Generating a SaaS Application report
- C. Enabling DoS protection
- D. Enabling packet buffer protection
Answer: B
Explanation:
TIPS & TRICKS: REDUCING MANAGEMENT PLANE LOAD:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClSvCAK TIPS & TRICKS: REDUCING MANAGEMENT PLANE LOAD—PART 2:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClU4CAK
NEW QUESTION 9
An engineer configures a specific service route in an environment with multiple virtual systems instead of using the inherited global service route configuration.
What type of service route can be used for this configuration?
- A. IPv6 Source or Destination Address
- B. Destination-Based Service Route
- C. IPv4 Source Interface
- D. Inherit Global Setting
Answer: C
Explanation:
https://docs.paloaltonetworks.com/pan-os/11-0/pan-os-admin/virtual-systems/customize-service-routes-for-a-vir
NEW QUESTION 10
Refer to the exhibit.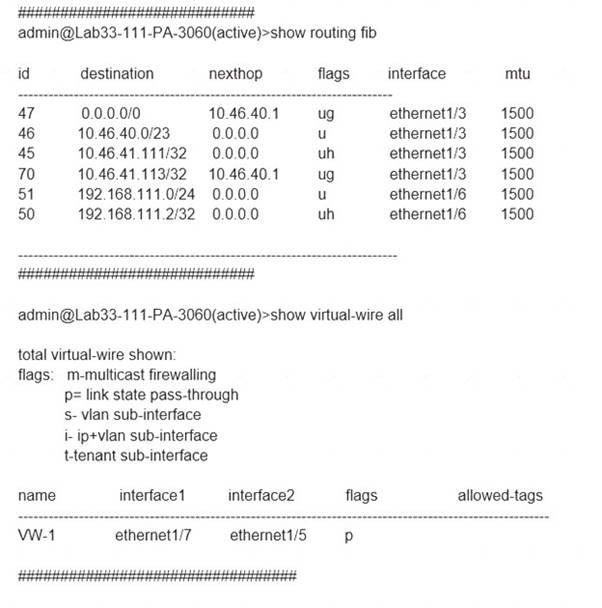
Which will be the egress interface if the traffic's ingress interface is ethernet1/7 sourcing from 192.168.111.3 and to the destination 10.46.41.113?
- A. ethernet1/6
- B. ethernet1/3
- C. ethernet1/7
- D. ethernet1/5
Answer: D
Explanation:
In the second image, VW ports mentioned are 1/5 and 1/7. Hence it can not be a part of any other routing. So if any traffic coming as ingress from 1/7, it has to go out via 1/5.
The egress interface for the traffic with ingress interface ethernet1/7, source 192.168.111.3, and destination 10.46.41.113 will be ethernet1/5. This is because the traffic will match the virtual wire with interfaces ethernet1/5 and ethernet1/7, which is configured to allow VLAN-tagged traffic with tags 10 and 201. The traffic will also match the security policy rule that allows traffic from zone Trust to zone Untrust, which are assigned to ethernet1/7 and ethernet1/5 respectively2. Therefore, the traffic will be forwarded to the same interface from which it was received, which is ethernet1/53.
NEW QUESTION 11
What can be used as an Action when creating a Policy-Based Forwarding (PBF) policy?
- A. Deny
- B. Discard
- C. Allow
- D. Next VR
Answer: B
Explanation:
Set the Action to take when matching a packet: Forward—Directs the packet to the specified Egress Interface.
Forward to VSYS (On a firewall enabled for multiple virtual systems)—Select the virtual system to which to forward the packet.
Discard—Drops the packet.
No PBF—Excludes packets that match the criteria for source, destination, application, or service defined in the rule. Matching packets use the route table instead of PBF; the firewall uses the route table to exclude the matched traffic from the redirected port.
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/policy/policy-based-forwarding/create-a-policy-ba
NEW QUESTION 12
Which three options does Panorama offer for deploying dynamic updates to its managed devices? (Choose three.)
- A. Check dependencies
- B. Schedules
- C. Verify
- D. Revert content
- E. Install
Answer: BDE
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-web-interface-help/panorama-web-interface/panorama-de https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-web-interface-help/panorama-web-interface/panorama-de
NEW QUESTION 13
Which three authentication types can be used to authenticate users? (Choose three.)
- A. Local database authentication
- B. PingID
- C. Kerberos single sign-on
- D. GlobalProtect client
- E. Cloud authentication service
Answer: ACE
Explanation:
The three authentication types that can be used to authenticate users are: A: Local database authentication. This is the authentication type that uses the local user database on the firewall or Panorama to store and verify user credentials1. C: Cloud authentication service. This is the authentication type that uses a cloud-based identity provider such as Okta, PingOne, or PingFederate, to authenticate users and provide SAML assertions to the firewall or Panorama2. E: Kerberos single sign-on. This is the authentication type that uses the Kerberos protocol to authenticate users who are logged in to a Windows domain and provide them with seamless access to resources on the firewall or Panorama3.
NEW QUESTION 14
A company has configured a URL Filtering profile with override action on their firewall. Which two profiles are needed to complete the configuration? (Choose two)
- A. SSL/TLS Service
- B. HTTP Server
- C. Decryption
- D. Interface Management
Answer: AD
Explanation:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClRdCAK https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/url-filtering/configure-url-filtering
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/url-filtering/allow-password-access-to-certain-site
NEW QUESTION 15
A network administrator configured a site-to-site VPN tunnel where the peer device will act as initiator None of the peer addresses are known
What can the administrator configure to establish the VPN connection?
- A. Set up certificate authentication.
- B. Use the Dynamic IP address type.
- C. Enable Passive Mode
- D. Configure the peer address as an FQDN.
Answer: B
Explanation:
When the peer device will act as the initiator and none of the peer addresses are known, the administrator can enable Passive Mode to establish the VPN connection. Passive Mode tells the firewall to wait for the peer device to initiate the VPN connection. The other options are incorrect. Option A, setting up certificate authentication, would require the administrator to know the peer device's certificate. Option C, using the Dynamic IP address type, would require the administrator to know the peer device's dynamic IP address.
Option D, configuring the peer address as an FQDN, would require the administrator to know the peer device's fully qualified domain name.
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClIGCA0
NEW QUESTION 16
A network security administrator wants to inspect HTTPS traffic from users as it egresses through a firewall to the Internet/Untrust zone from trusted network zones.
The security admin wishes to ensure that if users are presented with invalid or untrusted security certificates, the user will see an untrusted certificate warning.
What is the best choice for an SSL Forward Untrust certificate?
- A. A web server certificate signed by the organization's PKI
- B. A self-signed certificate generated on the firewall
- C. A subordinate Certificate Authority certificate signed by the organization's PKI
- D. A web server certificate signed by an external Certificate Authority
Answer: B
Explanation:  B is the best choice for an SSL Forward Untrust certificate because a self-signed certificate generated on the firewall is not trusted by any client browsers by default1. This means that if the firewall observes an invalid or untrusted security certificate from the server, it will present the self-signed certificate to the client, which will trigger an untrusted certificate warning2. This way, the security admin can ensure that users are aware of any potential risks when accessing HTTPS sites with untrusted certificates.
 A web server certificate signed by the organization’s PKI (A) or a subordinate Certificate Authority certificate signed by the organization’s PKI © are not good choices for an SSL Forward Untrust certificate because they are trusted by the client browsers that have the organization’s root CA installed1. This means that if the firewall observes an invalid or untrusted security certificate from the server, it will present the web server or subordinate CA certificate to the client, which will not trigger an untrusted certificate warning2. This way, the security admin cannot ensure that users are aware of any potential risks when accessing HTTPS sites with untrusted certificates. A web server certificate signed by an external Certificate Authority (D) is not a good choice for an SSL Forward Untrust certificate because it is trusted by most client browsers that have the external CA in
their trust store1. This means that if the firewall observes an invalid or untrusted security certificate from the server, it will present the web server certificate to the client, which will not trigger an untrusted certificate warning2. This way, the security admin cannot ensure that users are aware of any potential
risks when accessing HTTPS sites with untrusted certificates.
Verified References: 1: How to Configure SSL Decryption - Palo Alto Networks Knowledge Base 2: How to Implement and Test SSL Decryption - Palo Alto Networks Knowledge Base
NEW QUESTION 17
Which GloDalProtecI gateway setting is required to enable split-tunneting by access route, destination domain and application?
- A. Tunnel mode
- B. Satellite mode
- C. IPSec mode
- D. No Direct Access to local networks
Answer: A
Explanation:
https://docs.paloaltonetworks.com/globalprotect/9-1/globalprotect-admin/globalprotect-gateways/split-tunnel-tra
NEW QUESTION 18
Refer to the exhibit.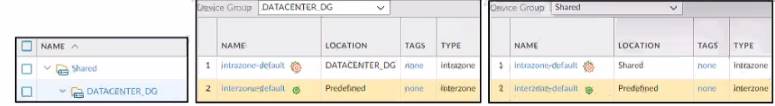
Based on the screenshots above what is the correct order in which the various rules are deployed to firewalls inside the DATACENTER_DG device group?
- A. shared pre-rules DATACENTER DG pre rulesrules configured locally on the firewall shared post-rules DATACENTER_DG post-rules DATACENTER.DG default rules
- B. shared pre-rules DATACENTER_DG pre-rulesrules configured locally on the firewall shared post-rulesDATACENTER.DG post-rules shared default rules
- C. shared pre-rules DATACENTER_DG pre-rulesrules configured locally on the firewall DATACENTER_DG post-rules shared post-rulesshared default rules
- D. shared pre-rules DATACENTER_DG pre-rulesrules configured locally on the firewall DATACENTER_DG post-rules shared post-rules DATACENTER_DG default rules
Answer: A
NEW QUESTION 19
......
100% Valid and Newest Version PCNSE Questions & Answers shared by Certshared, Get Full Dumps HERE: https://www.certshared.com/exam/PCNSE/ (New 294 Q&As)