Our pass rate is high to 98.9% and the similarity percentage between our 350-701 study guide and real exam is 90% based on our seven-year educating experience. Do you want achievements in the Cisco 350-701 exam in just one try? I am currently studying for the Cisco 350-701 exam. Latest Cisco 350-701 Test exam practice questions and answers, Try Cisco 350-701 Brain Dumps First.
Check 350-701 free dumps before getting the full version:
NEW QUESTION 1
A network engineer is deciding whether to use stateful or stateless failover when configuring two ASAs for high availability. What is the connection status in both cases?
- A. need to be reestablished with stateful failover and preserved with stateless failover
- B. preserved with stateful failover and need to be reestablished with stateless failover
- C. preserved with both stateful and stateless failover
- D. need to be reestablished with both stateful and stateless failover
Answer: B
NEW QUESTION 2
What is the term for when an endpoint is associated to a provisioning WLAN that is shared with guest access, and the same guest portal is used as the BYOD portal?
- A. single-SSID BYOD
- B. multichannel GUI
- C. dual-SSID BYOD
- D. streamlined access
Answer: C
NEW QUESTION 3
What is a difference between an XSS attack and an SQL injection attack?
- A. SQL injection is a hacking method used to attack SQL databases, whereas XSS attacks can exist in many different types of applications
- B. XSS is a hacking method used to attack SQL databases, whereas SQL injection attacks can exist in many different types of applications
- C. SQL injection attacks are used to steal information from databases whereas XSS attacks are used toredirect users to websites where attackers can steal data from them
- D. XSS attacks are used to steal information from databases whereas SQL injection attacks are used to redirect users to websites where attackers can steal data from them
Answer: C
Explanation:
In XSS, an attacker will try to inject his malicious code (usually malicious links) into a database. When other users follow his links, their web browsers are redirected to websites where attackers can steal data from them. In a SQL Injection, an attacker will try to inject SQL code (via his browser) into forms, cookies, or HTTP headers that do not use data sanitizing or validation methods of GET/POST parameters.
NEW QUESTION 4
Which Cisco security solution protects remote users against phishing attacks when they are not connected to the VPN?
- A. Cisco Stealthwatch
- B. Cisco Umbrella
- C. Cisco Firepower
- D. NGIPS
Answer: B
Explanation:
Cisco Umbrella protects users from accessing malicious domains by proactively analyzing and blocking unsafe destinations – before a connection is ever made. Thus it can protect from phishing attacks by blocking suspicious domains when users click on the given links that an attacker sent. Cisco Umbrella roaming protects your employees even when they are off the VPN.
NEW QUESTION 5
Drag and drop the steps from the left into the correct order on the right to enable AppDynamics to monitor an EC2 instance in Amazon Web Services.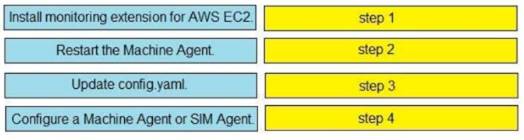
Solution:
Graphical user interface, text, application Description automatically generated
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 6
Which portion of the network do EPP solutions solely focus on and EDR solutions do not?
- A. server farm
- B. perimeter
- C. core
- D. East-West gateways
Answer: B
NEW QUESTION 7
What is a characteristic of Cisco ASA Netflow v9 Secure Event Logging?
- A. It tracks flow-create, flow-teardown, and flow-denied events.
- B. It provides stateless IP flow tracking that exports all records of a specific flow.
- C. It tracks the flow continuously and provides updates every 10 seconds.
- D. Its events match all traffic classes in parallel.
Answer: A
Explanation:
Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa92/configuration/general/asa-general-cli/ monitor-nsel.html
NEW QUESTION 8
Which feature is supported when deploying Cisco ASAv within AWS public cloud?
- A. multiple context mode
- B. user deployment of Layer 3 networks
- C. IPv6
- D. clustering
Answer: B
Explanation:
The ASAv on AWS supports the following features:+ Support for Amazon EC2 C5 instances, the next generation of the Amazon EC2 Compute Optimized instancefamily.+ Deployment in the Virtual Private Cloud (VPC)+ Enhanced networking (SR-IOV) where available+ Deployment from Amazon Marketplace+ Maximum of four vCPUs per instance+ User deployment of L3 networks+ Routed mode (default)Note: The Cisco Adaptive Security Virtual Appliance (ASAv) runs the same software as physical Cisco ASAs to deliver proven security functionality in a virtual form factor. The ASAv can be deployed in the public AWS cloud.It can then be configured to protect virtual and physical data center workloads that expand, contract, or shift their location over time. Reference:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa96/asav/quick-start-book/asav-96 qsg/asavaws.html
NEW QUESTION 9
An organization wants to use Cisco FTD or Cisco ASA devices. Specific URLs must be blocked from being accessed via the firewall which requires that the administrator input the bad URL categories that the organization wants blocked into the access policy. Which solution should be used to meet this requirement?
- A. Cisco ASA because it enables URL filtering and blocks malicious URLs by default, whereas Cisco FTD does not
- B. Cisco ASA because it includes URL filtering in the access control policy capabilities, whereas Cisco FTD does not
- C. Cisco FTD because it includes URL filtering in the access control policy capabilities, whereas Cisco ASA does not
- D. Cisco FTD because it enables URL filtering and blocks malicious URLs by default, whereas Cisco ASA does not
Answer: C
NEW QUESTION 10
What is a benefit of performing device compliance?
- A. Verification of the latest OS patches
- B. Device classification and authorization
- C. Providing multi-factor authentication
- D. Providing attribute-driven policies
Answer: A
NEW QUESTION 11
What is a benefit of conducting device compliance checks?
- A. It indicates what type of operating system is connecting to the network.
- B. It validates if anti-virus software is installed.
- C. It scans endpoints to determine if malicious activity is taking place.
- D. It detects email phishing attacks.
Answer: B
NEW QUESTION 12
A small organization needs to reduce the VPN bandwidth load on their headend Cisco ASA in order to
ensure that bandwidth is available for VPN users needing access to corporate resources on the10.0.0.0/24 local HQ network. How is this accomplished without adding additional devices to the
network?
- A. Use split tunneling to tunnel traffic for the 10.0.0.0/24 network only.
- B. Configure VPN load balancing to distribute traffic for the 10.0.0.0/24 network,
- C. Configure VPN load balancing to send non-corporate traffic straight to the internet.
- D. Use split tunneling to tunnel all traffic except for the 10.0.0.0/24 network.
Answer: A
NEW QUESTION 13
An engineer configures new features within the Cisco Umbrella dashboard and wants to identify and proxy traffic that is categorized as risky domains and may contain safe and malicious content. Which action accomplishes these objectives?
- A. Configure URL filtering within Cisco Umbrella to track the URLs and proxy the requests for those categories and below.
- B. Configure intelligent proxy within Cisco Umbrella to intercept and proxy the requests for only those categories.
- C. Upload the threat intelligence database to Cisco Umbrella for the most current information on reputations and to have the destination lists block them.
- D. Create a new site within Cisco Umbrella to block requests from those categories so they can be sent to the proxy device.
Answer: B
NEW QUESTION 14
Why is it important to implement MFA inside of an organization?
- A. To prevent man-the-middle attacks from being successful.
- B. To prevent DoS attacks from being successful.
- C. To prevent brute force attacks from being successful.
- D. To prevent phishing attacks from being successful.
Answer: C
NEW QUESTION 15
Drag and drop the posture assessment flow actions from the left into a sequence on the right.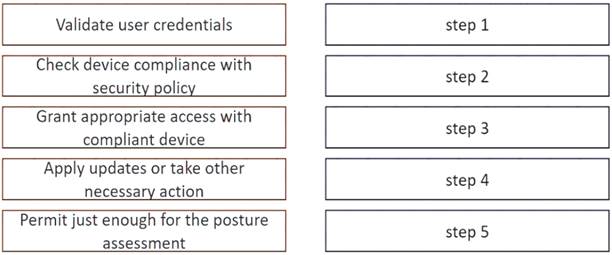
Solution:
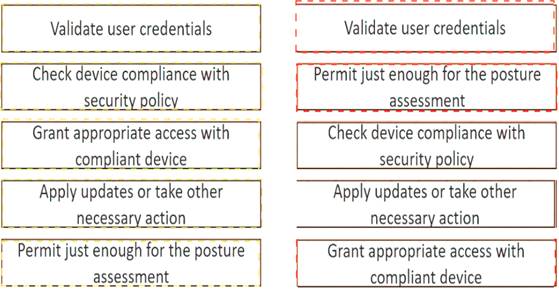
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 16
Which encryption algorithm provides highly secure VPN communications?
- A. 3DES
- B. AES 256
- C. AES 128
- D. DES
Answer: B
NEW QUESTION 17
Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?
- A. Cisco Tetration
- B. Cisco ISE
- C. Cisco AMP for Network
- D. Cisco AnyConnect
Answer: A
NEW QUESTION 18
An engineer musí set up 200 new laptops on a network and wants to prevent the users from moving their laptops around to simplify administration Which switch port MAC address security setting must be used?
- A. sticky
- B. static
- C. aging
- D. maximum
Answer: A
NEW QUESTION 19
Refer to the exhibit.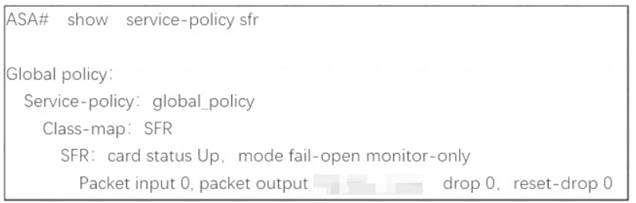
What are two indications of the Cisco Firepower Services Module configuration? (Choose two.)
- A. The module is operating in IDS mode.
- B. Traffic is blocked if the module fails.
- C. The module fails to receive redirected traffic.
- D. The module is operating in IPS mode.
- E. Traffic continues to flow if the module fails.
Answer: AE
Explanation:
sfr {fail-open | fail-close [monitor-only]} <- There's a couple different options here. The first one is fail-open which means that if the Firepower software module is unavailable, the ASA will continue to forward traffic. fail-close means that if the Firepower module fails, the traffic will stop flowing. While this doesn't seem ideal, there might be a use case for it when securing highly regulated environments. The monitor-only switch can be used with both and basically puts the Firepower services into IDS-mode only. This might be useful for initial testing or setup.
NEW QUESTION 20
......
P.S. Dumps-files.com now are offering 100% pass ensure 350-701 dumps! All 350-701 exam questions have been updated with correct answers: https://www.dumps-files.com/files/350-701/ (631 New Questions)