Our pass rate is high to 98.9% and the similarity percentage between our 350-701 study guide and real exam is 90% based on our seven-year educating experience. Do you want achievements in the Cisco 350-701 exam in just one try? I am currently studying for the Cisco 350-701 exam. Latest Cisco 350-701 Test exam practice questions and answers, Try Cisco 350-701 Brain Dumps First.
Cisco 350-701 Free Dumps Questions Online, Read and Test Now.
NEW QUESTION 1
What are two benefits of using Cisco Duo as an MFA solution? (Choose two.)
- A. grants administrators a way to remotely wipe a lost or stolen device
- B. provides simple and streamlined login experience for multiple applications and users
- C. native integration that helps secure applications across multiple cloud platforms or on-premises environments
- D. encrypts data that is stored on endpoints
- E. allows for centralized management of endpoint device applications and configurations
Answer: BC
NEW QUESTION 2
Which direction do attackers encode data in DNS requests during exfiltration using DNS tunneling?
- A. inbound
- B. north-south
- C. east-west
- D. outbound
Answer: D
NEW QUESTION 3
A company identified a phishing vulnerability during a pentest What are two ways the company can protect employees from the attack? (Choose two.)
- A. using Cisco Umbrella
- B. using Cisco ESA
- C. using Cisco FTD
- D. using an inline IPS/IDS in the network
- E. using Cisco ISE
Answer: AB
NEW QUESTION 4
Which cloud service offering allows customers to access a web application that is being hosted, managed, and maintained by a cloud service provider?
- A. IaC
- B. SaaS
- C. IaaS
- D. PaaS
Answer: B
NEW QUESTION 5
Which open standard creates a framework for sharing threat intelligence in a machine-digestible format?
- A. OpenC2
- B. OpenlOC
- C. CybOX
- D. STIX
Answer: D
NEW QUESTION 6
Which technology is used to improve web traffic performance by proxy caching?
- A. WSA
- B. Firepower
- C. FireSIGHT
- D. ASA
Answer: A
NEW QUESTION 7
What can be integrated with Cisco Threat Intelligence Director to provide information about security threats, which allows the SOC to proactively automate responses to those threats?
- A. Cisco Umbrella
- B. External Threat Feeds
- C. Cisco Threat Grid
- D. Cisco Stealthwatch
Answer: C
Explanation:
Reference:
https://blogs.cisco.com/developer/automate-threat-intelligence-using-cisco-threat-intelligencedirector
NEW QUESTION 8
Which two probes are configured to gather attributes of connected endpoints using Cisco Identity Services Engine? (Choose two)
- A. RADIUS
- B. TACACS+
- C. DHCP
- D. sFlow
- E. SMTP
Answer: AC
NEW QUESTION 9
Which two mechanisms are used to control phishing attacks? (Choose two)
- A. Enable browser alerts for fraudulent websites.
- B. Define security group memberships.
- C. Revoke expired CRL of the websites.
- D. Use antispyware software.
- E. Implement email filtering techniques.
Answer: AE
NEW QUESTION 10
An administrator needs to configure the Cisco ASA via ASDM such that the network management system can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration? (Choose two.)
- A. Specify the SNMP manager and UDP port.
- B. Specify an SNMP user group
- C. Specify a community string.
- D. Add an SNMP USM entry
- E. Add an SNMP host access entry
Answer: BE
NEW QUESTION 11
When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?
- A. Spero analysis
- B. dynamic analysis
- C. sandbox analysis
- D. malware analysis
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config-guidev60/Refere Spero analysis only uploads the signature of the (executable) files to the AMP cloud. It does not upload
thewhole file. Dynamic analysis sends files to AMP ThreatGrid.Dynamic Analysis submits (the whole) files to Cisco Threat Grid (formerly AMP Threat Grid). Cisco ThreatGrid runs the file in a sandbox environment, analyzes the file’s behavior to determine whether the file ismalicious, and returns a threat score that indicates the likelihood that a file contains malware. From the threatscore, you can view a dynamic analysis summary report with the reasons for the assigned threat score. Youcan also look in Cisco Threat Grid to view detailed reports for files that your organization submitted, as well asscrubbed reports with limited data for files that your organization did not submit.Local malware analysis allows a managed device to locally inspect executables, PDFs, office documents, andother types of files for the most common types of malware, using a detection rule set provided by the CiscoTalos Security Intelligence and Research Group (Talos). Because local analysis does not query the AMP cloud,and does not run the file, local malware analysis saves time and system resources. -> Malware analysis doesnot upload files to anywhere, it only checks the files locally.There is no sandbox analysis feature, it is just a method of dynamic analysis that runs suspicious files in avirtual machine.
NEW QUESTION 12
Which Dos attack uses fragmented packets to crash a target machine?
- A. smurf
- B. MITM
- C. teardrop
- D. LAND
Answer: C
Explanation:
A teardrop attack is a denial-of-service (DoS) attack that involves sending fragmented packets to a targetmachine. Since the machine receiving such packets cannot reassemble them due
to a bug in TCP/IPfragmentation reassembly, the packets overlap one another, crashing the target network device. This generally happens on older operating systems such as Windows 3.1x, Windows 95, Windows NT and versions of the Linux kernel prior to 2.1.63.
NEW QUESTION 13
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which
vulnerability allows the attacker to see the passwords being transmitted in clear text?
- A. weak passwords for authentication
- B. unencrypted links for traffic
- C. software bugs on applications
- D. improper file security
Answer: B
NEW QUESTION 14
Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?
- A. Cisco Identity Services Engine (ISE)
- B. Cisco Enterprise Security Appliance (ESA)
- C. Cisco Web Security Appliance (WSA)
- D. Cisco Advanced Stealthwatch Appliance (ASA)
Answer: C
NEW QUESTION 15
Which two are valid suppression types on a Cisco Next Generation Intrusion Prevention System? (Choose two)
- A. Port
- B. Rule
- C. Source
- D. Application
- E. Protocol
Answer: BC
NEW QUESTION 16
In which cloud services model is the tenant responsible for virtual machine OS patching?
- A. IaaS
- B. UCaaS
- C. PaaS
- D. SaaS
Answer: A
Explanation:
Only in On-site (on-premises) and IaaS we (tenant) manage O/S (Operating System).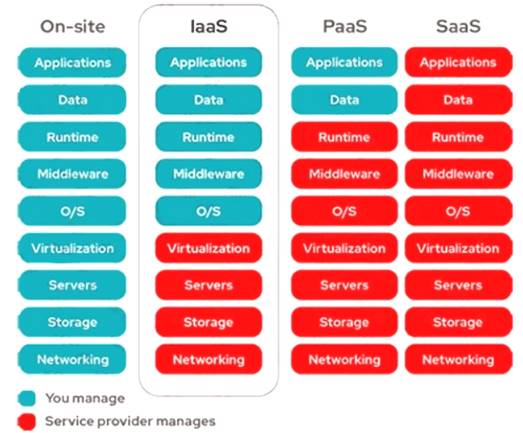
NEW QUESTION 17
A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address https://<FMC IP>/capure/CAPI/pcap/test.pcap, an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?
- A. Disable the proxy setting on the browser
- B. Disable the HTTPS server and use HTTP instead
- C. Use the Cisco FTD IP address as the proxy server setting on the browser
- D. Enable the HTTPS server for the device platform policy
Answer: D
NEW QUESTION 18
With regard to RFC 5176 compliance, how many IETF attributes are supported by the RADIUS CoA feature?
- A. 3
- B. 5
- C. 10
- D. 12
Answer: D
NEW QUESTION 19
What is a benefit of using GET VPN over FlexVPN within a VPN deployment?
- A. GET VPN supports Remote Access VPNs
- B. GET VPN natively supports MPLS and private IP networks
- C. GET VPN uses multiple security associations for connections
- D. GET VPN interoperates with non-Cisco devices
Answer: B
NEW QUESTION 20
......
Recommend!! Get the Full 350-701 dumps in VCE and PDF From Downloadfreepdf.net, Welcome to Download: https://www.downloadfreepdf.net/350-701-pdf-download.html (New 631 Q&As Version)