It is impossible to pass Cisco 350-701 exam without any help in the short term. Come to Pass4sure soon and find the most advanced, correct and guaranteed Cisco 350-701 practice questions. You will get a surprising result by our Renewal Implementing and Operating Cisco Security Core Technologies practice guides.
Check 350-701 free dumps before getting the full version:
NEW QUESTION 1
What are two workloaded security models? (Choose two)
- A. SaaS
- B. IaaS
- C. on-premises
- D. off-premises
- E. PaaS
Answer: CD
NEW QUESTION 2
Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)
- A. It must include the current date.
- B. It must reside in the trusted store of the WSA.
- C. It must reside in the trusted store of the endpoint.
- D. It must have been signed by an internal CA.
- E. it must contain a SAN.
Answer: AB
NEW QUESTION 3
What provides visibility and awareness into what is currently occurring on the network?
- A. CMX
- B. WMI
- C. Prime Infrastructure
- D. Telemetry
Answer: D
Explanation:
Reference: https://www.cisco.com/c/dam/en_us/about/doing_business/legal/service_descriptions/docs/activethreat-analytics
NEW QUESTION 4
An organization wants to improve its cybersecurity processes and to add intelligence to its data The organization wants to utilize the most current intelligence data for URL filtering, reputations, and vulnerability information that can be integrated with the Cisco FTD and Cisco WSA What must be done to accomplish these objectives?
- A. Create a Cisco pxGrid connection to NIST to import this information into the security products for policy use
- B. Create an automated download of the Internet Storm Center intelligence feed into the Cisco FTD and Cisco WSA databases to tie to the dynamic access control policies.
- C. Download the threat intelligence feed from the IETF and import it into the Cisco FTD and Cisco WSA databases
- D. Configure the integrations with Talos Intelligence to take advantage of the threat intelligence that it provides.
Answer: D
NEW QUESTION 5
Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?
- A. RSA SecureID
- B. Internal Database
- C. Active Directory
- D. LDAP
Answer: C
NEW QUESTION 6
Which two services must remain as on-premises equipment when a hybrid email solution is deployed? (Choose two)
- A. DDoS
- B. antispam
- C. antivirus
- D. encryption
- E. DLP
Answer: DE
Explanation:
Reference: https://www.cisco.com/c/dam/en/us/td/docs/security/ces/overview_guide/Cisco_Cloud_Hybrid_Email_Security
NEW QUESTION 7
An engineer is adding a Cisco router to an existing environment. NTP authentication is configured on all devices in the environment with the command ntp authentication-key 1 md5 Clsc427128380. There are two routers on the network that are configured as NTP servers for redundancy, 192.168.1.110 and 192.168.1.111. 192.168.1.110 is configured as the authoritative time source. What command must be configured on the new router to use 192.168.1.110 as its primary time source without the new router attempting to offer time to existing devices?
- A. ntp server 192.168.1.110 primary key 1
- B. ntp peer 192.168.1.110 prefer key 1
- C. ntp server 192.168.1.110 key 1 prefer
- D. ntp peer 192.168.1.110 key 1 primary
Answer: A
NEW QUESTION 8
What is managed by Cisco Security Manager?
- A. access point
- B. WSA
- C. ASA
- D. ESA
Answer: C
Explanation:
Reference: https://www.cisco.com/c/en/us/products/security/security-manager/index.html
NEW QUESTION 9
Which SNMPv3 configuration must be used to support the strongest security possible?
- A. asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv des ciscXXXXXXXX asa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy
- B. asa-host(config)#snmp-server group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXX asa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy
- C. asa-host(config)#snmpserver group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv 3des ciscXXXXXXXX asa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy
- D. asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXX asa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy
Answer: D
NEW QUESTION 10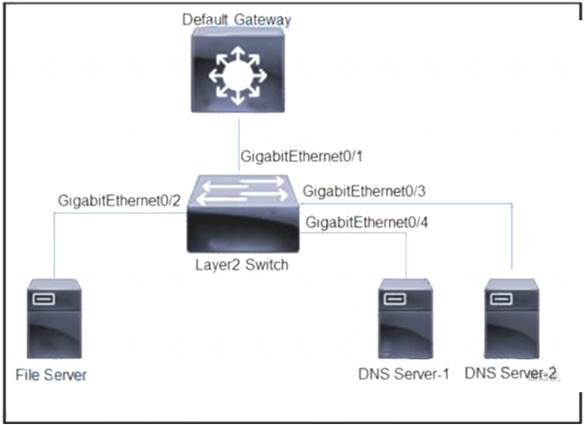
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?
- A. Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as isolated port, and GigabitEthernet0/3 and GigabitEthernet0/4 as promiscuous ports.
- B. Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as promiscuous port, Gigabit Ethernet0/3 and GigabitEthernet0/4 as isolated ports
- C. Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as isolated port and GigabitEthernet0/3 and GrgabitEthernet0/4 as community ports
- D. Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as community port, and GigabitEthernet0/3 and GrgabitEthernet0/4 as isolated ports.
Answer: C
NEW QUESTION 11
Drag and drop the exploits from the left onto the type of security vulnerability on the right.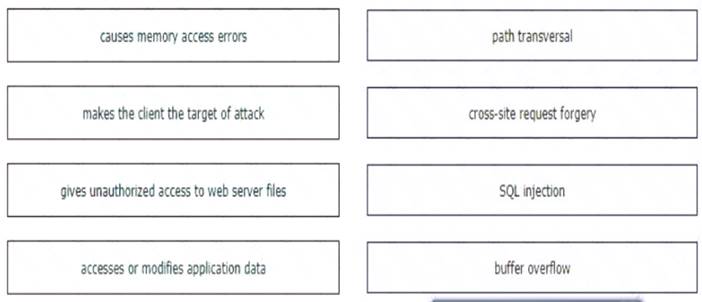
Solution:
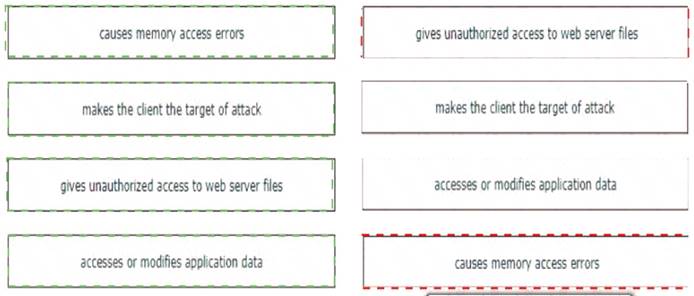
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 12
Refer to the exhibit.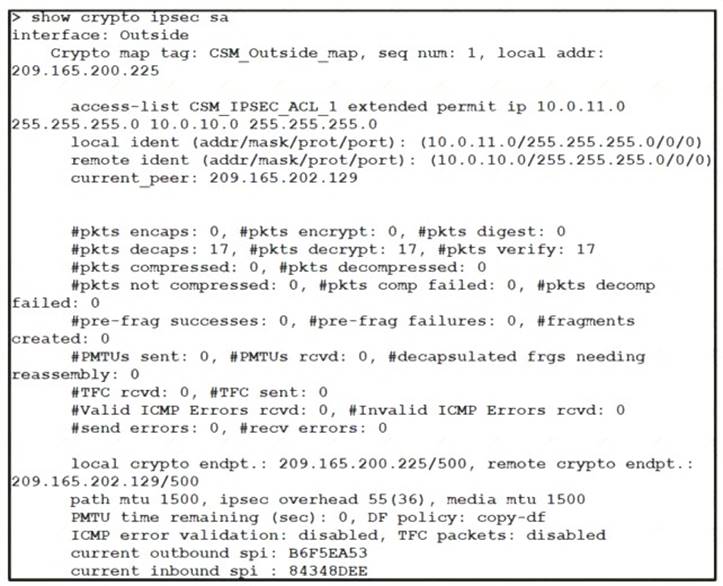
Traffic is not passing through IPsec site-to-site VPN on the Firepower Threat Defense appliance. What is causing this issue?
- A. No split-tunnel policy is defined on the Firepower Threat Defense appliance.
- B. The access control policy is not allowing VPN traffic in.
- C. Site-to-site VPN peers are using different encryption algorithms.
- D. Site-to-site VPN preshared keys are mismatched.
Answer: A
Explanation:
Reference: https://www.cisco.com/c/en/us/support/docs/security-vpn/ipsec-negotiation-ike-protocols/215470- site-to-site-vpn-configuration-on-ftd-ma.html
NEW QUESTION 13
Why is it important to have a patching strategy for endpoints?
- A. to take advantage of new features released with patches
- B. so that functionality is increased on a faster scale when it is used
- C. so that known vulnerabilities are targeted and having a regular patch cycle reduces risks
- D. so that patching strategies can assist with disabling nonsecure protocols in applications
Answer: C
NEW QUESTION 14
Which ASA deployment mode can provide separation of management on a shared appliance?
- A. DMZ multiple zone mode
- B. transparent firewall mode
- C. multiple context mode
- D. routed mode
Answer: C
NEW QUESTION 15
What are two benefits of Flexible NetFlow records? (Choose two)
- A. They allow the user to configure flow information to perform customized traffic identification
- B. They provide attack prevention by dropping the traffic
- C. They provide accounting and billing enhancements
- D. They converge multiple accounting technologies into one accounting mechanism
- E. They provide monitoring of a wider range of IP packet information from Layer 2 to 4
Answer: AD
Explanation:
Reference: https://www.cisco.com/en/US/docs/ios/fnetflow/configuration/guide/cust_fnflow_rec_mon_external_docbase_0 d9.html#wp1057997Note: Traditional NetFlow allows us to monitor from Layer 2 to 4 but Flexible NetFlow goes beyond theselayers.
NEW QUESTION 16
What is a language format designed to exchange threat intelligence that can be transported over the TAXII protocol?
- A. STIX
- B. XMPP
- C. pxGrid
- D. SMTP
Answer: A
Explanation:
TAXII (Trusted Automated Exchange of Indicator Information) is a standard that provides a transport
NEW QUESTION 17
Which Cisco product is open, scalable, and built on IETF standards to allow multiple security products from Cisco and other vendors to share data and interoperate with each other?
- A. Advanced Malware Protection
- B. Platform Exchange Grid
- C. Multifactor Platform Integration
- D. Firepower Threat Defense
Answer: B
Explanation:
With Cisco pxGrid (Platform Exchange Grid), your multiple security products can now share data and work together. This open, scalable, and IETF standards-driven platform helps you automate security to get answers and contain threats faster.
NEW QUESTION 18
An engineer integrates Cisco FMC and Cisco ISE using pxGrid Which role is assigned for Cisco FMC?
- A. client
- B. server
- C. controller
- D. publisher
Answer: D
NEW QUESTION 19
For a given policy in Cisco Umbrella, how should a customer block website based on a custom list?
- A. by specifying blocked domains in me policy settings
- B. by specifying the websites in a custom blocked category
- C. by adding the websites to a blocked type destination list
- D. by adding the website IP addresses to the Cisco Umbrella blocklist
Answer: C
NEW QUESTION 20
......
P.S. Easily pass 350-701 Exam with 631 Q&As Dumps-files.com Dumps & pdf Version, Welcome to Download the Newest Dumps-files.com 350-701 Dumps: https://www.dumps-files.com/files/350-701/ (631 New Questions)