Cause all that matters here is passing the Cisco 300-715 exam. Cause all that you need is a high score of 300-715 Implementing and Configuring Cisco Identity Services Engine (SISE) exam. The only one thing you need to do is downloading Actualtests 300-715 exam study guides now. We will not let you down with our money-back guarantee.
Online Cisco 300-715 free dumps demo Below:
NEW QUESTION 1
An administrator is adding a switch to a network that is running Cisco ISE and is only for IP Phones The phones do not have the ability to authenticate via 802 1X Which command is needed on each switch port for authentication?
- A. dot1x system-auth-control
- B. enable bypass-mac
- C. enable network-authentication
- D. mab
Answer: D
Explanation:
https://www.cisco.com/en/US/docs/ios-xml/ios/sec_usr_aaa/configuration/15-2mt/sec-config-mab.html
NEW QUESTION 2
An engineer is configuring ISE for network device administration and has devices that support both protocols. What are two benefits of choosing TACACS+ over RADUs for these devices? (Choose two.)
- A. TACACS+ is FIPS compliant while RADIUS is not
- B. TACACS+ is designed for network access control while RADIUS is designed for role-based access.
- C. TACACS+ uses secure EAP-TLS while RADIUS does not.
- D. TACACS+ provides the ability to authorize specific commands while RADIUS does not
- E. TACACS+ encrypts the entire payload being sent while RADIUS only encrypts the password.
Answer: DE
NEW QUESTION 3
What are two benefits of TACACS+ versus RADIUS for device administration? (Choose two )
- A. TACACS+ supports 802.1X, and RADIUS supports MAB
- B. TACACS+ uses UDP, and RADIUS uses TCP
- C. TACACS+ has command authorization, and RADIUS does not.
- D. TACACS+ provides the service type, and RADIUS does not
- E. TACACS+ encrypts the whole payload, and RADIUS encrypts only the password.
Answer: CE
NEW QUESTION 4
An engineer is configuring posture assessment for their network access control and needs to use an agent that supports using service conditions as conditions for the assessment. The agent should be run as a background process to avoid user interruption but when it is run. the user can see it. What is the problem?
- A. The engineer is using the "Anyconnect” posture agent but should be using the "Stealth Anyconnect posture agent
- B. The posture module was deployed using the headend instead of installing it with SCCM
- C. The user was in need of remediation so the agent appeared m the notifications
- D. The proper permissions were no! given to the temporal agent to conduct the assessment
Answer: A
NEW QUESTION 5
What is a restriction of a standalone Cisco ISE node deployment?
- A. Only the Policy Service persona can be disabled on the node.
- B. The domain name of the node cannot be changed after installation.
- C. Personas are enabled by default and cannot be edited on the node.
- D. The hostname of the node cannot be changed after installation.
Answer: C
NEW QUESTION 6
What is a requirement for Feed Service to work?
- A. TCP port 3080 must be opened between Cisco ISE and the feed server
- B. Cisco ISE has a base license.
- C. Cisco ISE has access to an internal server to download feed update
- D. Cisco ISE has Internet access to download feed update
Answer: C
NEW QUESTION 7
Refer to the exhibit.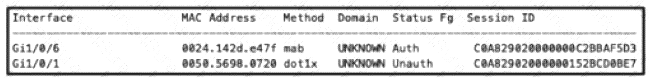
An engineer is configuring a client but cannot authenticate to Cisco ISE During troubleshooting, the show authentication sessions command was issued to display the authentication status of each port Which command gives additional information to help identify the problem with the authentication?
- A. show authentication sessions
- B. show authentication sessions Interface Gil/0/1 output
- C. show authentication sessions interface Gi1/0/1 details
- D. show authentication sessions output
Answer: C
NEW QUESTION 8
What is the maximum number of PSN nodes supported in a medium-sized deployment?
- A. three
- B. five
- C. two
- D. eight
Answer: B
NEW QUESTION 9
Which two authentication protocols are supported by RADIUS but not by TACACS+? (Choose two.)
- A. MSCHAPv1
- B. PAP
- C. EAP
- D. CHAP
- E. MSCHAPV2
Answer: CE
NEW QUESTION 10
An engineer is configuring 802.1X and is testing out their policy sets. After authentication, some endpoints are given an access-reject message but are still allowed onto the network. What is causing this issue to occur?
- A. The switch port is configured with authentication event server dead action authorize vlan.
- B. The authorization results for the endpoints include a dACL allowing access.
- C. The authorization results for the endpoints include the Trusted security group tag.
- D. The switch port is configured with authentication open.
Answer: D
NEW QUESTION 11
What is a valid guest portal type?
- A. Sponsored-Guest
- B. My Devices
- C. Sponsor
- D. Captive-Guest
Answer: A
NEW QUESTION 12
If a user reports a device lost or stolen, which portal should be used to prevent the device from accessing the network while still providing information about why the device is blocked?
- A. Client Provisioning
- B. Guest
- C. BYOD
- D. Blacklist
Answer: D
Explanation:
https://www.cisco.com/c/en/us/td/docs/solutions/Enterprise/Borderless_Networks/Unified_Access/BYOD_Desi The Blacklist identity group is system generated and maintained by ISE to prevent access to lost or stolen devices. In this design guide, two authorization profiles are used to enforce the permissions for wireless and wired devices within the Blacklist: Blackhole WiFi Access Blackhole Wired Access
NEW QUESTION 13
Drag the Cisco ISE node types from the left onto the appropriate purposes on the right.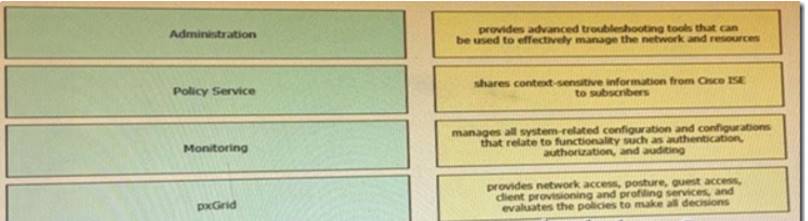
Solution:
Monitoring = provides advanced monitoring and troubleshooting tools that you can use to effectively manage your network and resources
Policy Service = provides network access, posture, guest access, client provisioning, and profiling services. This persona evaluates the policies and makes all the decisions.
Administration = manages all system-related configuration and configurations that relate to functionality such as authentication, authorization, auditing, and so on
pxGrid = shares context-sensitive information from Cisco ISE to subscribers https://www.cisco.com/c/en/us/td/docs/security/ise/1-4/admin_guide/b_ise_admin_guide_14/b_ise_admin_guide
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 14
An engineer is creating a new authorization policy to give the endpoints access to VLAN 310 upon successful authentication The administrator tests the 802.1X authentication for the endpoint and sees that it is authenticating successfully What must be done to ensure that the endpoint is placed into the correct VLAN?
- A. Configure the switchport access vlan 310 command on the switch port
- B. Ensure that the security group is not preventing the endpoint from being in VLAN 310
- C. Add VLAN 310 in the common tasks of the authorization profile
- D. Ensure that the endpoint is using The correct policy set
Answer: C
NEW QUESTION 15
When configuring an authorization policy, an administrator cannot see specific Active Directory groups present in their domain to be used as a policy condition. However, other groups that are in the same domain are seen What is causing this issue?
- A. Cisco ISE only sees the built-in groups, not user created ones
- B. The groups are present but need to be manually typed as conditions
- C. Cisco ISE's connection to the AD join point is failing
- D. The groups are not added to Cisco ISE under the AD join point
Answer: D
Explanation:
https://www.youtube.com/watch?v=0kuEZEo564s&ab_channel=CiscoISE-IdentityServicesEngine
NEW QUESTION 16
......
P.S. Downloadfreepdf.net now are offering 100% pass ensure 300-715 dumps! All 300-715 exam questions have been updated with correct answers: https://www.downloadfreepdf.net/300-715-pdf-download.html (238 New Questions)