Want to know Pass4sure 300-715 Exam practice test features? Want to lear more about Cisco Implementing and Configuring Cisco Identity Services Engine (SISE) certification experience? Study Certified Cisco 300-715 answers to Refresh 300-715 questions at Pass4sure. Gat a success with an absolute guarantee to pass Cisco 300-715 (Implementing and Configuring Cisco Identity Services Engine (SISE)) test on your first attempt.
Free demo questions for Cisco 300-715 Exam Dumps Below:
NEW QUESTION 1
Which two Cisco ISE deployment models require two nodes configured with dedicated PAN and MnT personas? (Choose two.)
- A. three PSN nodes
- B. seven PSN nodes with one PxGrid node
- C. five PSN nodes with one PxGrid node
- D. two PSN nodes with one PxGrid node
- E. six PSN nodes
Answer: CD
NEW QUESTION 2
Which Cisco ISE deployment model is recommended for an enterprise that has over 50,000 concurrent active endpoints?
- A. large deployment with fully distributed nodes running all personas
- B. medium deployment with primary and secondary PAN/MnT/pxGrid nodes with shared PSNs
- C. medium deployment with primary and secondary PAN/MnT/pxGrid nodes with dedicated PSNs
- D. small deployment with one primary and one secondary node running all personas
Answer: C
NEW QUESTION 3
Which two endpoint compliance statuses are possible? (Choose two.)
- A. unknown
- B. known
- C. invalid
- D. compliant
- E. valid
Answer: AD
NEW QUESTION 4
What must be configured on the WLC to configure Central Web Authentication using Cisco ISE and a WLC?
- A. Set the NAC State option to SNMP NAC.
- B. Set the NAC State option to RADIUS NAC.
- C. Use the radius-server vsa send authentication command.
- D. Use the ip access-group webauth in command.
Answer: B
NEW QUESTION 5
A network security engineer needs to configure 802.1X port authentication to allow a single host to be authenticated for data and another single host to be authenticated for voice. Which command should the engineer run on the interface to accomplish this goal?
- A. authentication host-mode single-host
- B. authentication host-mode multi-auth
- C. authentication host-mode multi-host
- D. authentication host-mode multi-domain
Answer: D
NEW QUESTION 6
Which two default endpoint identity groups does Cisco ISE create? (Choose two )
- A. block list
- B. endpoint
- C. profiled
- D. allow list
- E. unknown
Answer: CE
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-1/admin_guide/b_ise_admin_guide_21/b_ise_admin_guide
Default Endpoint Identity Groups Created for EndpointsCisco ISE creates the following five endpoint identity groups by default: Blacklist, GuestEndpoints, Profiled, RegisteredDevices, and Unknown. In addition, it creates two more identity groups, such as Cisco-IP-Phone and Workstation, which are associated to the Profiled (parent) identity group. A parent group is the default identity group that exists in the system.
Cisco ISE creates the following endpoint identity groups: Blacklist—This endpoint identity group includes endpoints that are statically assigned to this group in Cisco ISE and endpoints that are block listed in the device registration portal. An authorization profile can be defined in Cisco ISE to permit, or deny network access to endpoints in this group. GuestEndpoints—This endpoint identity group includes endpoints that are used by guest users. Profiled—This endpoint identity group includes endpoints that match endpoint profiling policies except Cisco IP phones and workstations in Cisco ISE. RegisteredDevices—This endpoint identity group includes endpoints, which are registered devices that are added by an employee through the devices registration portal. The profiling service continues to profile these devices normally when they are assigned to this group. Endpoints are statically assigned to this group in Cisco ISE, and the profiling service cannot reassign them to any other identity group. These devices will appear like any other endpoint in the endpoints list. You can edit, delete, and block these devices that you added through the device registration portal from the endpoints list in the Endpoints page in Cisco ISE. Devices that you have blocked in the device registration portal are assigned to the Blacklist endpoint identity group, and an authorization profile that exists in Cisco ISE redirects blocked devices to a URL, which displays “Unauthorised Network Access”, a default portal page to the blocked devices. Unknown—This endpoint identity group includes endpoints that do not match any profile in Cisco ISE. In addition to the above system created endpoint identity groups, Cisco ISE creates the following endpoint
identity groups, which are associated to the Profiled identity group: Cisco-IP-Phone—An identity group that contains all the profiled Cisco IP phones on your network. Workstation—An identity group that contains all the profiled workstations on your network.
NEW QUESTION 7
Which Cisco ISE deployment model provides redundancy by having every node in the deployment configured with the Administration. Policy Service, and Monitoring personas to protect from a complete node failure?
- A. distributed
- B. dispersed
- C. two-node
- D. hybrid
Answer: C
NEW QUESTION 8
Which two features should be used on Cisco ISE to enable the TACACS+ feature? (Choose two )
- A. External TACACS Servers
- B. Device Admin Service
- C. Device Administration License
- D. Server Sequence
- E. Command Sets
Answer: BC
NEW QUESTION 9
A network engineer has been tasked with enabling a switch to support standard web authentication for Cisco ISE. This must include the ability to provision for URL redirection on authentication Which two commands must be entered to meet this requirement? (Choose two)
- A. Ip http secure-authentication
- B. Ip http server
- C. Ip http redirection
- D. Ip http secure-server
- E. Ip http authentication
Answer: BD
Explanation:
https://www.cisco.com/en/US/docs/switches/lan/catalyst3850/software/release/3.2_0_se/multibook/configuratio
NEW QUESTION 10
Which port does Cisco ISE use for native supplicant provisioning of a Windows laptop?
- A. TCP 8909
- B. TCP 8905
- C. UDP 1812
- D. TCP 443
Answer: B
NEW QUESTION 11
A new employee just connected their workstation to a Cisco IP phone. The network administrator wants to ensure that the Cisco IP phone remains online when the user disconnects their Workstation from the corporate network Which CoA configuration meets this requirement?
- A. Port Bounce
- B. Reauth
- C. NoCoA
- D. Disconnect
Answer: C
Explanation:
https://ciscocustomer.lookbookhq.com/iseguidedjourney/ISE-profiling-design
NEW QUESTION 12
A network administrator is configuring a secondary cisco ISE node from the backup configuration of the primary cisco ISE node to create a high availability pair The Cisco ISE CA certificates and keys must be manually backed up from the primary Cisco ISE and copied into the secondary Cisco ISE Which command most be issued for this to work?
- A. copy certificate Ise
- B. application configure Ise
- C. certificate configure Ise
- D. Import certificate Ise
Answer: B
Explanation:
https://community.cisco.com/t5/network-access-control/ise-certificate-import-export/m-p/3847746
NEW QUESTION 13
Drag the steps to configure a Cisco ISE node as a primary administration node from the left into the correct order on the night.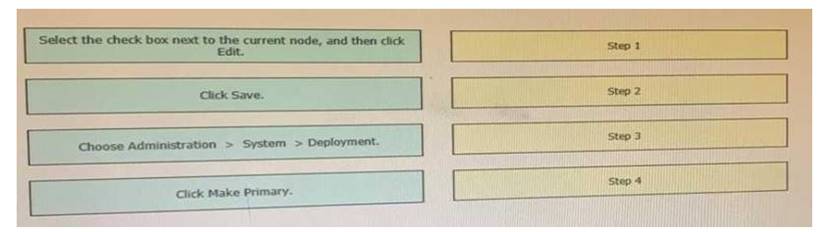
Solution:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-4/admin_guide/b_ise_admin_guide_24/b_ise_admin_guide
Step 1
Choose Administration > System > Deployment.
The Register button will be disabled initially. To enable this button, you must configure a Primary PAN.
Step 2
Check the check box next to the current node, and click Edit.
Step 3
Click Make Primary
to configure your Primary PAN.
Step 4
Enter data on the General Settings
Step 5
tab.
Click Save to save the node configuration.
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 14
A Cisco ISE administrator must restrict specific endpoints from accessing the network while in closed mode. The requirement is to have Cisco ISE centrally store the endpoints to restrict access from. What must be done to accomplish this task''
- A. Add each MAC address manually to a blocklist identity group and create a policy denying access
- B. Create a logical profile for each device's profile policy and block that via authorization policies.
- C. Create a profiling policy for each endpoint with the cdpCacheDeviceld attribute.
- D. Add each IP address to a policy denying access.
Answer: B
NEW QUESTION 15
An organization wants to improve their BYOD processes to have Cisco ISE issue certificates to the BYOD endpoints. Currently, they have an active certificate authority and do not want to replace it with Cisco ISE. What must be configured within Cisco ISE to accomplish this goal?
- A. Create a certificate signing request and have the root certificate authority sign it.
- B. Add the root certificate authority to the trust store and enable it for authentication.
- C. Create an SCEP profile to link Cisco ISE with the root certificate authority.
- D. Add an OCSP profile and configure the root certificate authority as secondary.
Answer: C
Explanation:
Ref:https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine-software/116068-configure-pr
NEW QUESTION 16
......
Recommend!! Get the Full 300-715 dumps in VCE and PDF From Certleader, Welcome to Download: https://www.certleader.com/300-715-dumps.html (New 238 Q&As Version)