we provide 100% Correct Cisco 300-715 practice exam which are the best for clearing 300-715 test, and to get certified by Cisco Implementing and Configuring Cisco Identity Services Engine (SISE). The 300-715 Questions & Answers covers all the knowledge points of the real 300-715 exam. Crack your Cisco 300-715 Exam with latest dumps, guaranteed!
Also have 300-715 free dumps questions for you:
NEW QUESTION 1
When configuring Active Directory groups, what does the Cisco ISE use to resolve ambiguous group names?
- A. MIB
- B. TGT
- C. OMAB
- D. SID
Answer: D
NEW QUESTION 2
An organization wants to split their Cisco ISE deployment to separate the device administration functionalities from the mam deployment. For this to work, the administrator must deregister any nodes that will become a part of the new deployment, but the button for this option is grayed out Which configuration is causing this behavior?
- A. One of the nodes is an active PSN.
- B. One of the nodes is the Primary PAN
- C. All of the nodes participate in the PAN auto failover.
- D. All of the nodes are actively being synched.
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/ise/2-7/admin_guide/b_ise_27_admin_guide/b_ISE_admin_27_
NEW QUESTION 3
An administrator is adding network devices for a new medical building into Cisco ISE. These devices must be in a network device group that is identifying them as "Medical Switch" so that the policies can be made separately for the endpoints connecting through them. Which configuration item must be changed in the network device within Cisco ISE to accomplish this goal?
- A. Change the device type to Medical Switch.
- B. Change the device profile to Medical Switch.
- C. Change the model name to Medical Switch.
- D. Change the device location to Medical Switch.
Answer: A
NEW QUESTION 4
An administrator is configuring a switch port for use with 802 1X What must be done so that the port will allow voice and multiple data endpoints?
- A. Configure the port with the authentication host-mode multi-auth command
- B. Connect the data devices to the port, then attach the phone behind them.
- C. Use the command authentication host-mode multi-domain on the port
- D. Connect a hub to the switch port to allow multiple devices access after authentication
Answer: A
NEW QUESTION 5
What is a difference between TACACS+ and RADIUS in regards to encryption?
- A. TACACS+ encrypts only the password, whereas RADIUS encrypts the username and password.
- B. TACACS+ encrypts the username and password, whereas RADIUS encrypts only the password.
- C. TACACS+ encrypts the password, whereas RADIUS sends the entire packet in clear text.
- D. TACACS+ encrypts the entire packet, whereas RADIUS encrypts only the password.
Answer: D
NEW QUESTION 6
Drag the descriptions on the left onto the components of 802.1X on the right.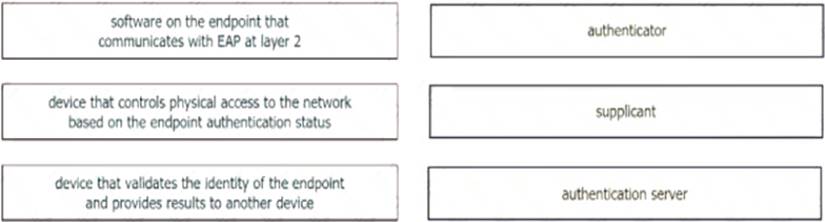
Solution:
https://netlabz.wordpress.com/2016/09/24/cisco-ise-fundamentals/
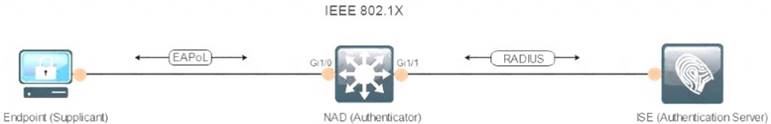
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 7
Which type of identity store allows for creating single-use access credentials in Cisco ISE?
- A. OpenLDAP
- B. Local
- C. PKI
- D. RSA SecurID
Answer: D
NEW QUESTION 8
Which two actions occur when a Cisco ISE server device administrator logs in to a device? (Choose two)
- A. The device queries the internal identity store
- B. The Cisco ISE server queries the internal identity store
- C. The device queries the external identity store
- D. The Cisco ISE server queries the external identity store.
- E. The device queries the Cisco ISE authorization server
Answer: AD
NEW QUESTION 9
While configuring Cisco TrustSec on Cisco IOS devices the engineer must set the CTS device ID and password in order for the devices to authenticate with each other. However after this is complete the devices are not able to property authenticate What issue would cause this to happen even if the device ID and passwords are correct?
- A. The device aliases are not matching
- B. The 5GT mappings have not been defined
- C. The devices are missing the configuration cts credentials trustsec verify 1
- D. EAP-FAST is not enabled
Answer: B
NEW QUESTION 10
An engineer is configuring Cisco ISE policies to support MAB for devices that do not have 802.1X capabilities. The engineer is configuring new endpoint identity groups as conditions to be used in the AuthZ policies, but noticed that the endpoints are not hitting the correct policies. What must be done in order to get the devices into the right policies?
- A. Manually add the MAC addresses of the devices to endpoint ID groups in the context visibility database.
- B. Create an AuthZ policy to identify Unknown devices and provide partial network access prior to profiling.
- C. Add an identity policy to dynamically add the IP address of the devices to their endpoint identity groups.
- D. Identify the non 802.1X supported device types and create custom profiles for them to profile into.
Answer: D
NEW QUESTION 11
An administrator replaced a PSN in the distributed Cisco ISE environment. When endpoints authenticate to it, the devices are not getting the right profiles or attributes and as a result, are not hitting the correct policies. This was working correctly on the previous PSN. Which action must be taken to ensure the endpoints get identified?
- A. Verify that the MnT node is tracking the session.
- B. Verify the shared secret used between the switch and the PSN.
- C. Verify that the profiling service is running on the new PSN.
- D. Verify that the authentication request the PSN is receiving is not malformed.
Answer: C
NEW QUESTION 12
An engineer is configuring web authentication using non-standard ports and needs the switch to redirect traffic to the correct port. Which command should be used to accomplish this task?
- A. permit tcp any any eq <port number>
- B. aaa group server radius proxy
- C. ip http port <port number>
- D. aaa group server radius
Answer: C
NEW QUESTION 13
A Cisco ISE administrator needs to ensure that guest endpoint registrations are only valid for one day When testing the guest policy flow, the administrator sees that the Cisco ISE does not delete the endpoint in the Guest Endpoints identity store after one day and allows access to the guest network after that period. Which configuration is causing this problem?
- A. The Endpoint Purge Policy is set to 30 days for guest devices
- B. The RADIUS policy set for guest access is set to allow repeated authentication of the same device
- C. The length of access is set to 7 days in the Guest Portal Settings
- D. The Guest Account Purge Policy is set to 15 days
Answer: A
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/ise/1-3/admin_guide/b_ise_admin_guide_13/b_ise_admin_guide
NEW QUESTION 14
What are two differences of TACACS+ compared to RADIUS? (Choose two.)
- A. TACACS+ uses a connectionless transport protocol, whereas RADIUS uses a connection-oriented transport protocol.
- B. TACACS+ encrypts the full packet payload, whereas RADIUS only encrypts the password.
- C. TACACS+ only encrypts the password, whereas RADIUS encrypts the full packet payload.
- D. TACACS+ uses a connection-oriented transport protocol, whereas RADIUS uses a connectionless transport protocol.
- E. TACACS+ supports multiple sessions per user, whereas RADIUS supports one session per user.
Answer: BD
NEW QUESTION 15
An organization has a fully distributed Cisco ISE deployment When implementing probes, an administrator must scan for unknown endpoints to learn the IP-to-MAC address bindings. The scan is complete on one FPSN. but the information is not available on the others. What must be done to make the information available?
- A. Scanning must be initiated from the PSN that last authenticated the endpoint
- B. Cisco ISE must learn the IP-MAC binding of unknown endpoints via DHCP profiling, not via scanning
- C. Scanning must be initiated from the MnT node to centrally gather the information
- D. Cisco ISE must be configured to learn the IP-MAC binding of unknown endpoints via RADIUS authentication, not via scanning
Answer: B
NEW QUESTION 16
......
Recommend!! Get the Full 300-715 dumps in VCE and PDF From Allfreedumps.com, Welcome to Download: https://www.allfreedumps.com/300-715-dumps.html (New 238 Q&As Version)